When we die, it's not just physical estates that need to be settled, an entire digital footprint survives us. So what do Apple and Google do with that data?
Article URL: https://z.ai/blog/glm-legal Comments URL: https://news.ycombinator.com/item?id=50058507 Points: 9 # Comments: 0
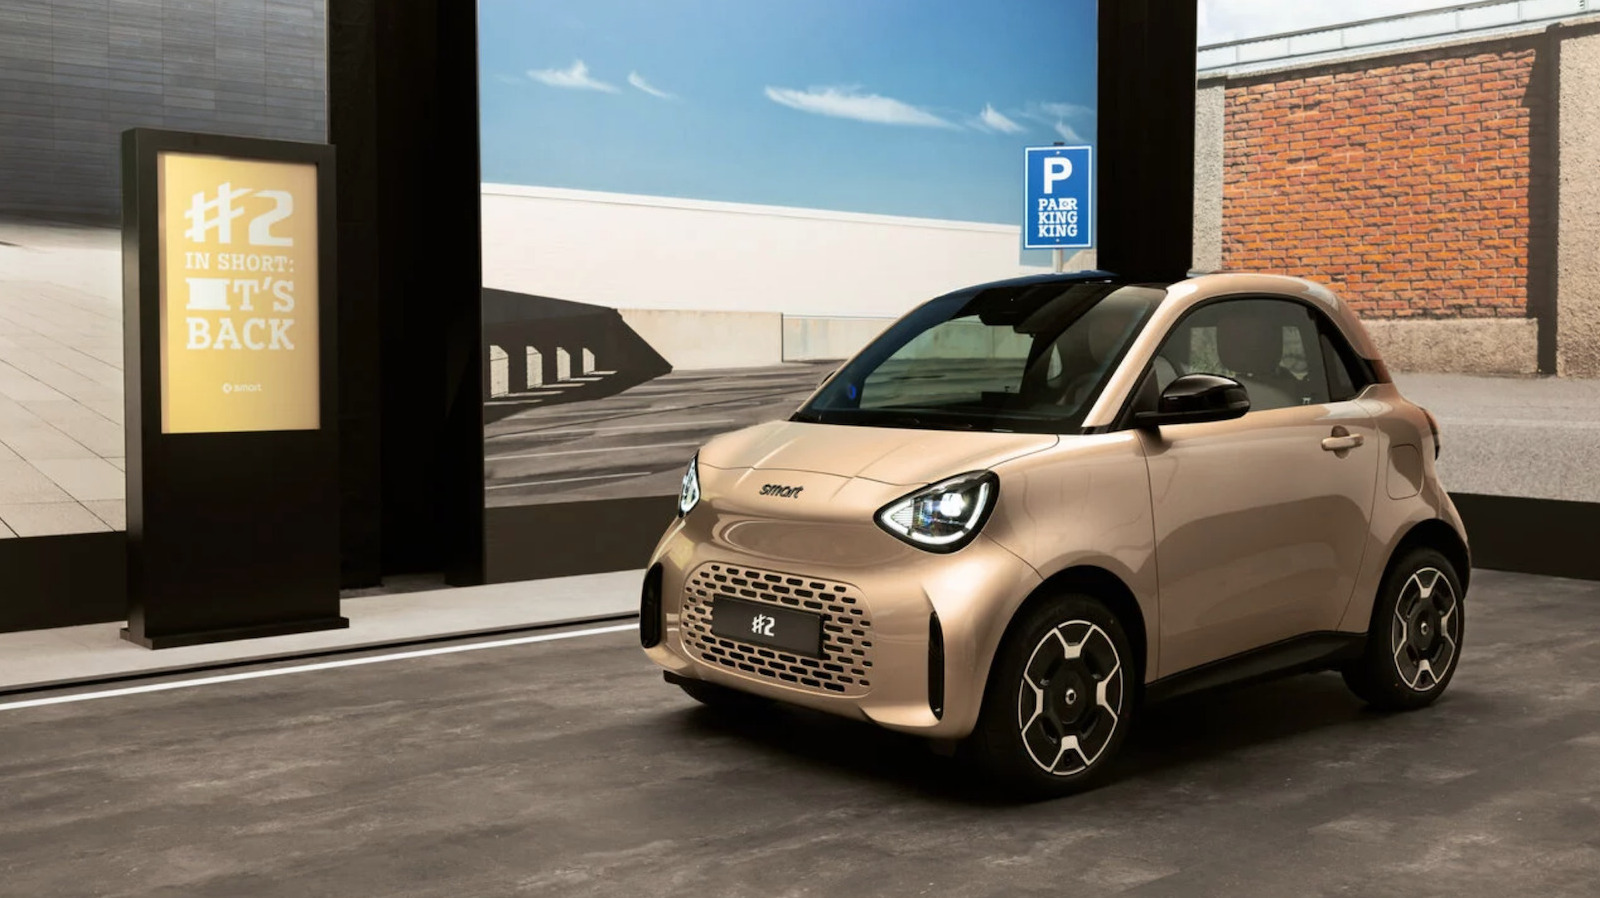
Sadly we won't be seeing whatever this car inspires stateside.
PM Burnham confirms talks in Brussels next month, insisting the British public will be 'the boss' of the reset.

Australia close on statement victory over South Africa in Durban after Matt Renshaw's dream Test continues.

Opposition parties say revisions to the list of eligible voters favor Prime Minister Narendra Modi's party. Authorities have removed more than 130 million names from the voter roll.
A little car with decent mileage per charge.
Article URL: https://kettlehour.com/ Comments URL: https://news.ycombinator.com/item?id=50058235 Points: 1 # Comments: 0
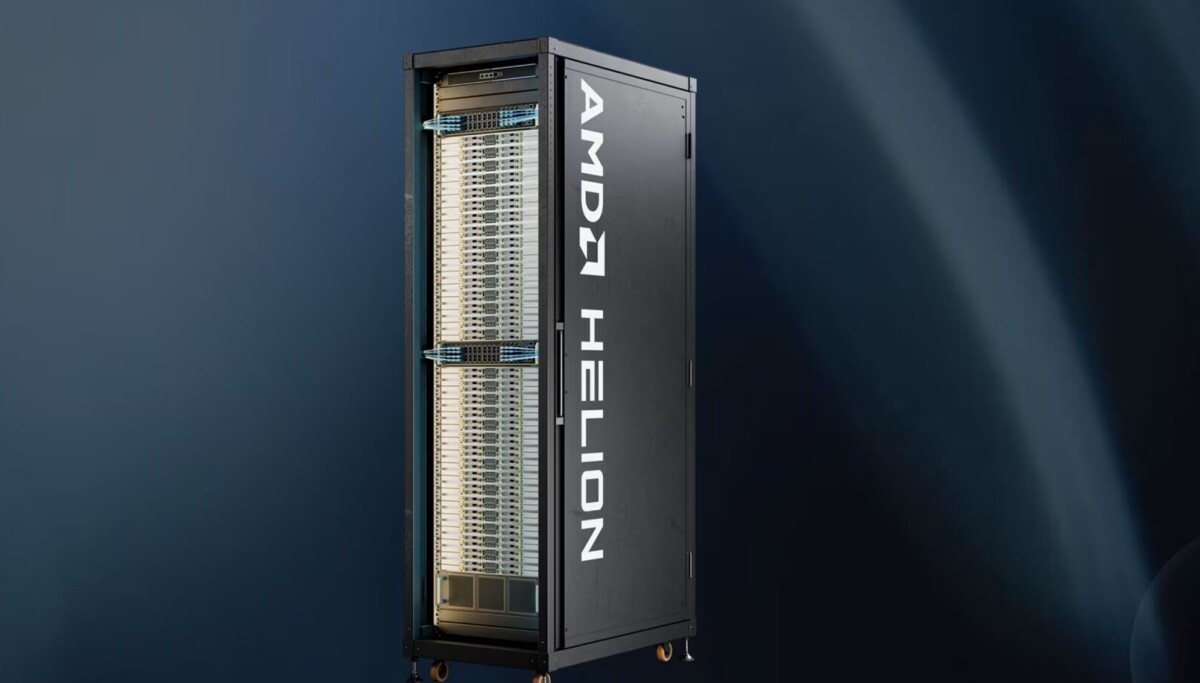
CPU-only and mixed CPU/GPU configurations due from partners in November
The BBC's Dan Johnson reports from Kyiv, where Ukrainians face another winter with electricity outages.

Introducing Boole-1.7B, a 1-bit version of Qwen3-1.7B. Boole-1.7B retains 85.9% of BF16 performance using 247MB (13.9x smaller). It outperforms 1-bit Bonsai-1.7B and similar-sized LFM models, and nearly matches 1.58-bit Bonsai-1.7B. It’s intended for English, non-thinking use. To learn more, - Blog: https://precisionnumerics.ai/blog/boole-1p7b - Weights: https://huggingface.co/precision-numerics/Boole-1.7B - Chat in browser: https://precisionnumerics.ai/chat/ We're going to ship more capable models soon for the open-source community. Let us know what models/capabilities you want to see next…

Officials say a staff member disarmed the suspect, who hid a hunting shotgun in a guitar case, before police arrived.

Article URL: https://vibealternatives.com/ Comments URL: https://news.ycombinator.com/item?id=50058127 Points: 12 # Comments: 8
Backing the genocide case against Myanmar must be followed by concrete action to protect the Rohingya.

The prime minister says Iran's Islamic Revolutionary Guard "almost certainly" directed the RAF Fairford incident.

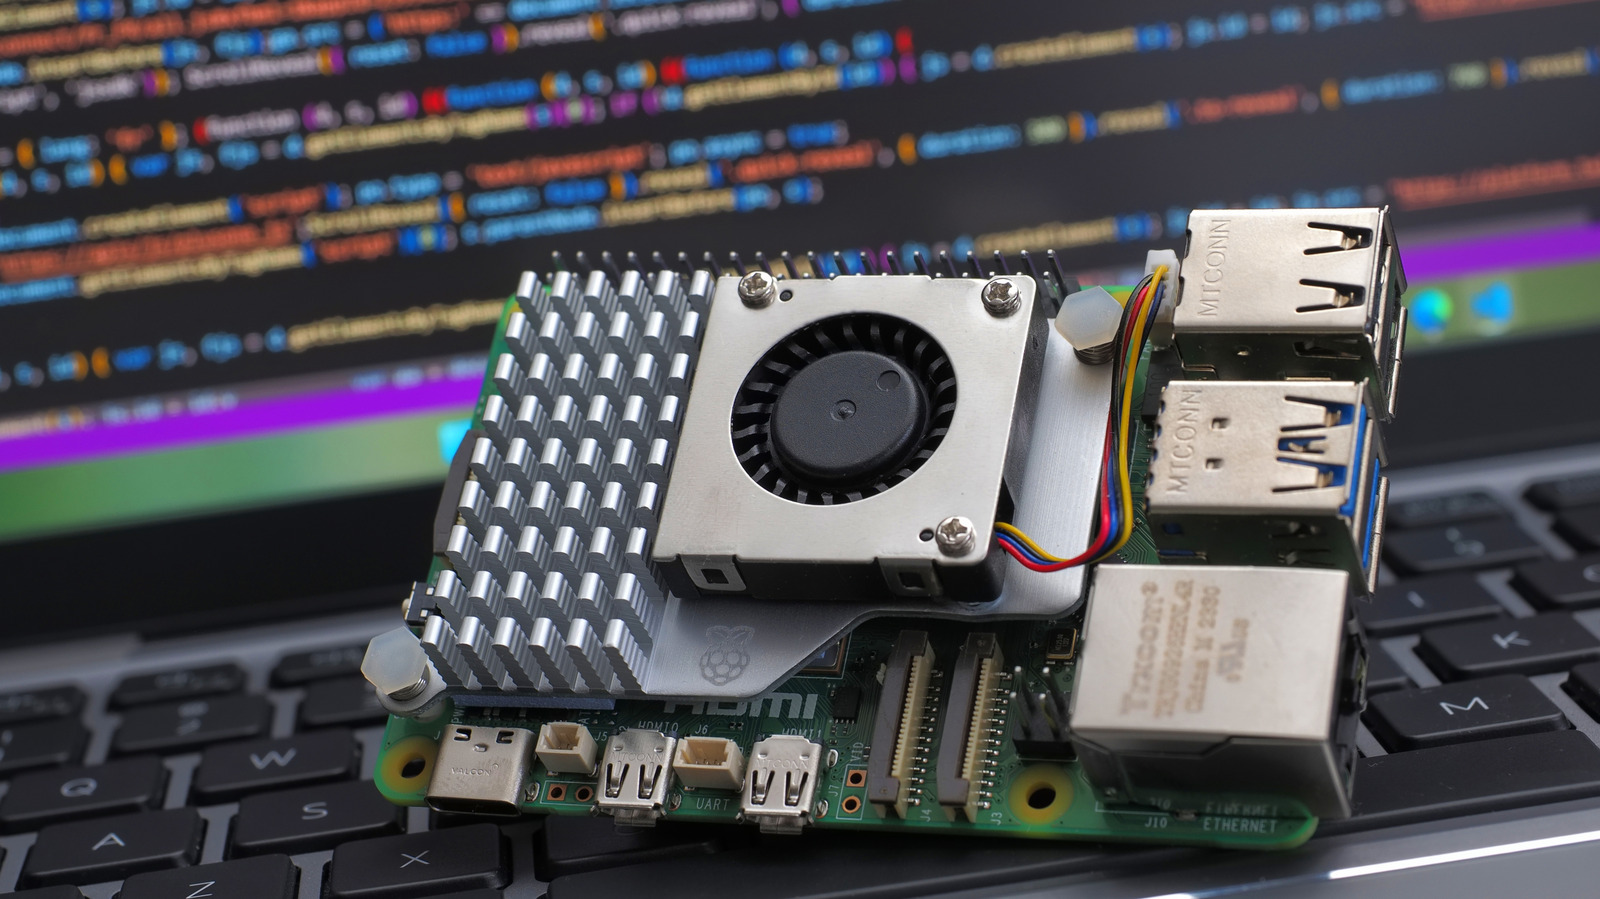
Raspberry Pi boards have helped hobbyists get computing projects started for very little money down. However, knowing how much memory is needed can be tricky.
Could AI actually make PR better?

There are a few settings to check if you're having issues with your map's location accuracy.
Article URL: https://www.cenntre.com Comments URL: https://news.ycombinator.com/item?id=50058075 Points: 2 # Comments: 0
Multiple Ukrainian drone strikes over the last week have taken Russian data centers offline and reportedly caused online bot traffic to plummet - but in reality it's probably not the kind of bot activity most people associate with Russia. A chart citing Cloudflare data has been circulating around social media platforms, showing a sharp decline […]

Article URL: https://tellcut.app/studio Comments URL: https://news.ycombinator.com/item?id=50058060 Points: 1 # Comments: 0
Hey HN, I’m Oskar, one of the co-founders of TesterArmy. We built an agentic testing framework for web and mobile because traditional testing frameworks can’t keep up with the pace of how we build software today. e2e allows you to mix deterministic and agentic APIs in the same test. You can write the test cases using familiar APIs like getByText()or getByTestId() which you can also mix it with agentic agent.act(). The unique part about it is that e2e will cache and replay the agentic actions so you don’t have to pay for AI on each run. You can use it with any LLM, including subscr…
Article URL: https://uk.finance.yahoo.com/news/french-supermarket-chains-cyberattack-forced-115141288.html Comments URL: https://news.ycombinator.com/item?id=50057956 Points: 5 # Comments: 2
Microsoft President Brad Smith calls for urgent AI regulation, saying milk and washing machines have more oversight than AI companies.
Article URL: https://llamachord.com/ Comments URL: https://news.ycombinator.com/item?id=50057880 Points: 1 # Comments: 1
Deadly air raids on gold miners in Sudan expose deepening border lawlessness and regional instability.

submitted by /u/fattyfoods [link] [comments]
Blueprints AI, a bootstrapped startup based in Santa Monica, developed software that produces code-compliant construction blueprints from a photo, PDF, or sketch.

Plumes of black smoke rise from a Petro Dolphin oil tanker by a drone attack off the coast of Oman.

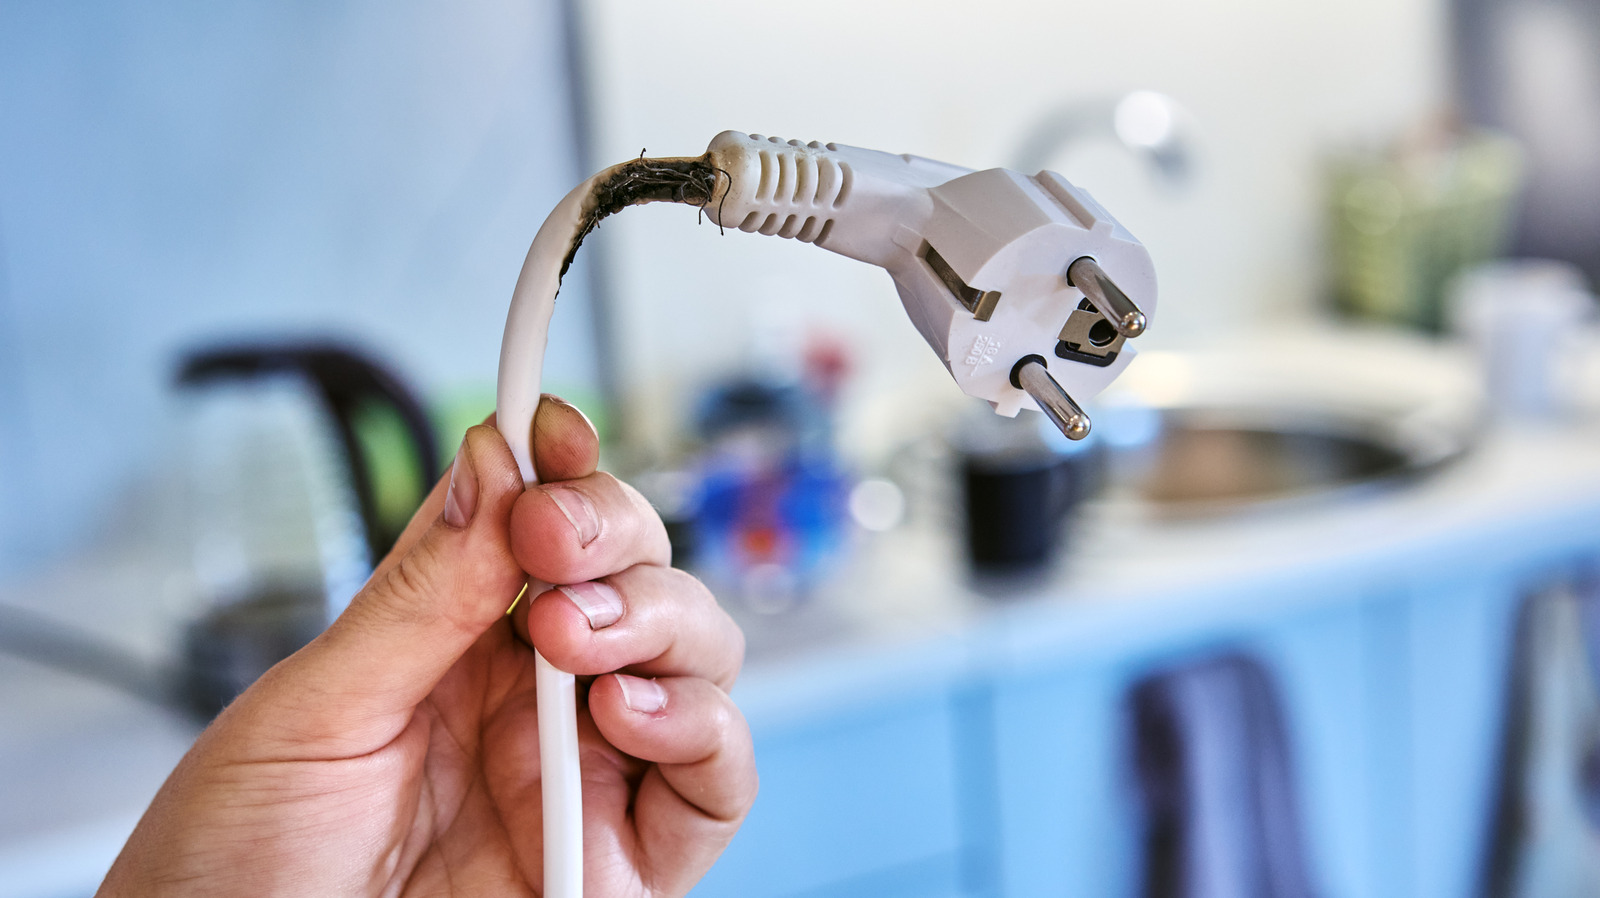
An extension cord may seem like a permanent solution to a problem, but they aren't designed for long-term use, so leaving them plugged in can have consequences.
England batter Ollie Pope pulls out of the draft for the Afghanistan Premier League.

Google’s newest wearable costs $179.99 and has a sleek feel like the Fitbit Air but with an OLED display.

Article URL: https://www.bbc.com/news/articles/crq5nzxv9q4yo Comments URL: https://news.ycombinator.com/item?id=50057551 Points: 5 # Comments: 3

Washington's position on Ukraine remains ambivalent while losses mount and an energy crisis deepens.

In September, hackers from a group called ShinyHunters announced that they stole a trove of FBI data about its own agents. It was an intelligence disaster . Last week, the FBI arrested (alternate link ) someone associated with that crime.
US authorities searched the Democratic congresswoman’s home as part of a criminal investigation.

submitted by /u/existentialthrust [link] [comments]

Article URL: https://azure.microsoft.com/en-us/blog/deep-dive-into-azure-maia-300-architecture/ Comments URL: https://news.ycombinator.com/item?id=50057185 Points: 8 # Comments: 1
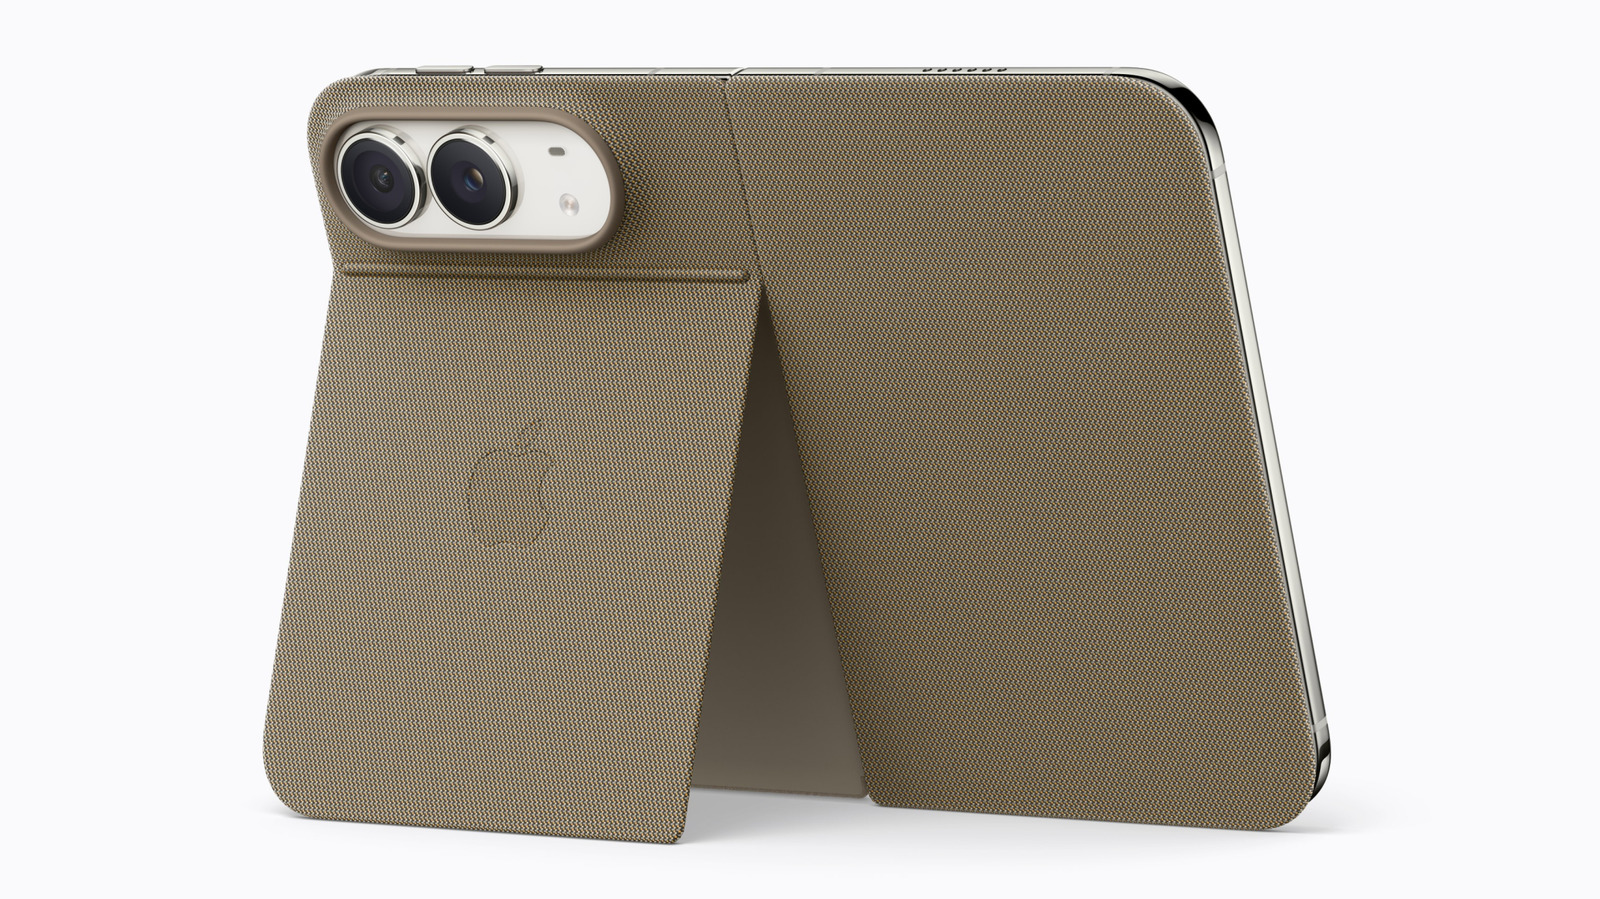
The iPhone Duo's foldable design changes what accessories fit. Here's what to know about cases, chargers, screen protectors, mounts, and more.
Also, F1’s final sprint saw our first real wet racing of the year.
Tehran seeks dialogue in Yemen conflict, warning a military solution risks complicating the volatile regional situation.

The IRGC is hitting more ships allegedly part of a shuttle operation to move crude oil beyond the Strait of Hormuz.

The attacks mark the deadliest assault on Saudi soil in more than a decade.

After defending his Japan Open title after returning from injury, Alcaraz never found his rhythm in a scrappy contest.

Goldberg was a regular Al Jazeera contributor and died after a long battle with colon cancer, his family said.

Atletico vs Man United and Man City vs PSG headline the league's match day two action as the competition returns.

An Israeli settler was filmed abusing and reportedly poisoning livestock in the village of Al-Mughayyir.

Anger is growing in Azerbaijan after girls wearing hijabs were barred from schools under new uniform rules.

The blast occurred in northern Israel near the Lebanese border and is under investigation.

The head of the International Energy Agency, Fatih Birol, discusses the challenges facing the global economy.

The Fitbit Edge offers more than the Air, but it's not a real smartwatch.
Article URL: https://www.theguardian.com/technology/2026/oct/12/ai-less-regulated-than-milk-microsoft-president-calls-for-tougher-rules Comments URL: https://news.ycombinator.com/item?id=50055654 Points: 17 # Comments: 20
The Swedish academy says the academics' models are 'now used by central banks and governments around the world'.

Fahmida Y Rashid will keep the momentum going as she leads Dark Reading.
Popular former general Zaluzhnyi leads potential challengers, alongside intelligence chief Budanov and reformer Fedorov.

From creative wordplay on song lyrics to simply calling Man City 'cheats', the Reds fans went all out at Anfield.

Snap vote could bring PP, Vox to power as polls show falling support for Sanchez, one of Europe's last leftist leaders.

When Israel orders an evacuation of Gaza City, a journalist documents the displacement while living it with her family.

Protests have broken out as some schools begin preventing students and teachers from attending classes.

The personal AI agents rollout is going about as smoothly as expected: Amazon now blocks Meta's Muse because it doesn't identify itself as a bot while browsing; Instinct keeps raising privacy concerns; and the horror stories from pretty much every personal AI agent keep piling up. Regardless, the tech world is mesmerized by the capabilities and potential of these services. Less than a year
Trump's energy truce sparks criticism over aiding Russia's war finances amid diesel shortages and rising consumer costs.

Cryptocurrency hardware maker Ledger has temporarily paused sales of its products via CryptoBilis following reports of stolen funds linked to devices sold by the reseller. On Friday, the company said it was investigating reports of loss of funds from users in Southeast Asia who had purchased products from CryptoBilis. The incident is said to have resulted in losses totaling more than $86
Article URL: https://blog.julik.nl/2026/10/the-weimar-of-ruby Comments URL: https://news.ycombinator.com/item?id=50054474 Points: 6 # Comments: 0
Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure. The vulnerability, tracked as CVE-2026-102255 (CVSS score: 10.0), is a case of pre-authenticated server-side request forgery (SSRF) that could allow a remote attacker "to direct the appliance to issue requests on their
A maximum-severity security flaw impacting the Bricksforge plugin for WordPress has come under active exploitation in the wild, according to Patchstack. The critical vulnerability in question is CVE-2026-85097 (CVSS score: 10.0), which allows unauthenticated attackers to upload and execute arbitrary PHP code on vulnerable WordPress websites, resulting in remote code execution (RCE). The
Article URL: https://simonkoeck.com/writeups/google-devsite-flask-session-pickle-rce Comments URL: https://news.ycombinator.com/item?id=50052638 Points: 19 # Comments: 4
Cybersecurity researchers have disclosed details of a two-pronged artificial intelligence (AI)-augmented initial access campaign targeting WordPress sites, e-commerce platforms, and critical infrastructure entities in Ukraine. The activity, which brings together commodity offensive tools like Cobalt Strike with an AI orchestration layer powered by Anthropic's Claude Code, has been attributed
China's $7.5 billion EU hybrid boom faces new curbs under China-EU deal Reuters
Shares shrug off oil swings as earnings season looms Reuters
Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. "Compared with the variants we usually observe, P7 reduces its on-device footprint, adds on-device keychain and crypto-wallet theft, and adds two way C2 communication with the attacker's infrastructure," iVerify said in a new report published Thursday. The name
As streamers poach viral creators to appeal to children, digital whack-a-mole has become a new kind of family challenge Exasperated dad Simon Hooper shakes his fist at the camera in a viral video . “We managed to get rid of YouTube in our household six months ago and the kids are finally OK with it,” he says – but Netflix is “now commissioning YouTubers to make their brain rot and putting it back in front of my kids’ faces”. The precise “brain rot” he’s referring to is the arrival of a polarising show that’s lighting up parent chats around the globe. And while Salish and J…
In environments studied for the 2026 State of Agent Security Report, roughly 1,280 third-party products now embed AI. About 282 of them sit behind single sign-on. The other thousand are invisible to identity infrastructure by default, not because anyone hid them, but because an identity stack can only govern what authenticates through it, and most agents never do. That gap is the clearest
Anthropic on Friday said it's cutting off live internet access for all its internal evaluations until further notice following the discovery of new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior and targeted real websites. The AI company said it identified four broad categories of unintended model actions during evaluations and internal use of Claude
Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved the FBI of sensitive data on thousands of agents, multiple sources tell KrebsOnSecurity.
The attack on the British retailer shows that compromising a single identity can lead to much deeper penetration of the corporate network.
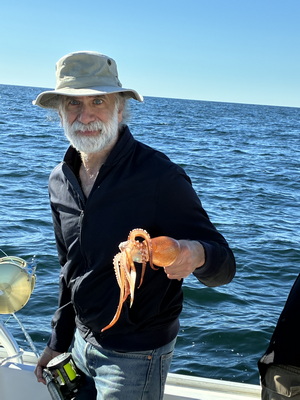
On Wednesday I spent a day fishing, on a small boat out of Gloucester, MA. We caught many cod (none of which we could keep), and a bunch of hake and mackerel (all of which we could keep). And…I caught a squid! Near as I can tell, it’s a longfin squid, sometimes called a Boston squid ( Doryteuthis (Amerigo) pealeii ). That night I cooked it over a barbecue grill—hot and fast. Delicious.
Welcome to another gangbuster year for strategic M&A activity in cyber, with 117 deals announced in the latest quarter. What's different: Many of the buyers are not your typical cybersecurity firms.
Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over 340 repositories. "Using the account of Takashi Kitao, author of the 18,400-star game engine pyxel, the attacker pushed a malicious workflow to 27 repositories starting at 13:20 UTC," StepSecurity
The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X. ShinyHunters is the extortion group that said in September it had breached the FBI's jobs portal and stolen sensitive data on almost all FBI agents and job applicants. The FBI has not named the suspect, and no charges have been made public. The
In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from the arrest of a suspected ShinyHunters operative to the compromise of a Pentagon-run data center.
📢 DEF CON Training is now accepting course submissions for 2027! Whether you're an experienced instructor or bringing a new course to the community, we're looking for high-quality, hands-on training that helps security professionals build real-world skills. Submit your training material today for the opportunity to teach alongside the DEF CON community in locations around the world including Las Vegas, the Middle East, and Singapore! For more details, see the application. The deadline to apply is November 13, 2026. Apply here today 🔗 Already submitted your course for Singapore March 202…

Those closest to executives must match their security postures because the weakest link in a family can become the entry point for attacks.
Whether it’s a super-glowy serum or a cult gardening tool, here are our writers’ favourite buys from the past year • Don’t get the Filter delivered to your inbox? Sign up here The Filter is turning two! To celebrate, we asked our contributors for their favourite products from the past year, and rounded up the team’s picks too. From handbag-sized umbrellas and stylish yet practical wellies to reading lights and luxurious duvets, these are the products that stood out. Continue reading...
Four more U.S. states sued router maker TP-Link Systems on October 6, bringing the total to five, with Texas filing a suit in February. Florida, Iowa, Montana and Nebraska allege the California company misled buyers about how secure its routers are and how separate it is from China. TP-Link denies the claims and says it will fight them in court. TP-Link Systems is based in
As AI agents gain authority over business systems, attackers can manipulate them like business email compromise (BEC) victims.
Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection. AnyDesk patched the flaw in version 8.0.3 in June, but its changelog described the fix only as "fixed a bug that could lead to a crash," with no CVE assigned and no security
Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI). "It's an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing," Anthropic said. "Projects that join will receive thorough, periodic security scans by our strongest models at no cost."
Threat actors have been observed exploiting two recently disclosed flaws in the AhsayCBS backup utility to seize control of affected devices and deploy web shells and XMRig cryptocurrency miners. Details of the flaws are below - CVE-2026-105133 (CVSS v4 score: 5.5) - An improper authentication vulnerability in the checkSysPwd() function in the "com/ahsay/obs/api/ApiStructsAction.java"
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon. The vulnerabilities in question are listed below - CVE-2015-3306 (CVSS score: 10.0) - An improper access control vulnerability in ProFTPD that could allow
As enterprises race to deploy autonomous AI agents to accelerate business, a new report reveals they are tethered to security architectures built for a different era. The "Horizons of Identity Security" report from SailPoint highlights a critical “velocity paradox,” in which organizations invest in AI-speed business operations while continuing to rely on human-speed security controls, creating a
A bug in GoBalance, a tool many dark-web sites use to stay reachable during attacks, lets anyone work out the secret key that controls a site's .onion address using only public information, and then take that address over. Searchlight Cyber, which disclosed the flaw on October 8, says an attacker who recovers the key can redirect the site's visitors to a copy of the site they control.
Three research teams broke into Google's Pixel 10 on October 8 at Pwn2Own Ireland, a hacking contest in Cork whose rules require every target to be fully patched. The contest pays researchers to show working exploits and passes the flaws to the vendors. One of the three Pixel exploits earned Ikotas Labs $300,000, the contest's top prize, and made the team the overall winner. Trend Micro's Zero
Citrix has released patches for yet another critical security flaw impacting NetScaler ADC and NetScaler Gateway that could result in remote code execution or denial-of-service (DoS) under certain conditions. "CVE-2026-107406 is a memory overflow vulnerability that may lead to remote code execution or denial-of-service under specific configuration conditions," Citrix said. The vulnerability
The U.S. Federal Bureau of Investigation (FBI) and Department of Justice (DoJ) have announced the disruption of malicious tools used by a China-linked advanced persistent threat group known as Flax Typhoon. To that end, the agencies seized several domains and blocked access to platforms that were used to scan, and in some cases infiltrate, U.S. critical infrastructure. The list of seized
A now-patched vulnerability in AWS Bedrock AgentCore could have allowed an attacker to use one AI chatbot to take over an organization's entire fleet.